Table of Contents
Opening: the pressing contradiction
The machines that carve tunnels and haul ore must be both open to command and closed to compromise; this is the paradox that drives operators to seek a robust fleet management solution. Problem-driven thinking begins by naming the fracture: safety and productivity depend on data and remote control, yet every connection is an invitation. Decades of collective engineering practice in telematics underpin the approach below, which isolates problems so they can be solved without ceremony.
Problem diagnosis: what breaks first
Three failures reappear across sites:- Unauthorized remote commands that risk physical harm.- Data leaks exposing location, load manifests, and personnel movements.- Access sprawl where too many accounts have broad privileges.You see the same pattern whether a loader works a pit or a truck travels a haul road: weak authentication, lax segmentation, and poor lifecycle controls. The consequences are immediate — safety incidents, regulatory exposure, and costly downtime.
Root causes: why existing systems fail
Failures arise from concrete technical and organizational gaps:- Legacy telematics modules designed before current threat models.- Over-reliance on perimeter defenses while internal services trust one another.- Manual onboarding and infrequent credential rotation.These are not abstractions. At major logistics nodes such as the Port of Rotterdam, operators learned that simple device-level compromise can cascade into entire fleet paralysis. Recognize the source; then remove it.

Technical controls that mend the fracture
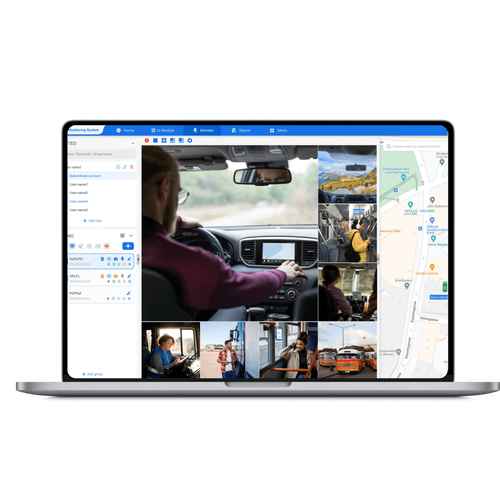
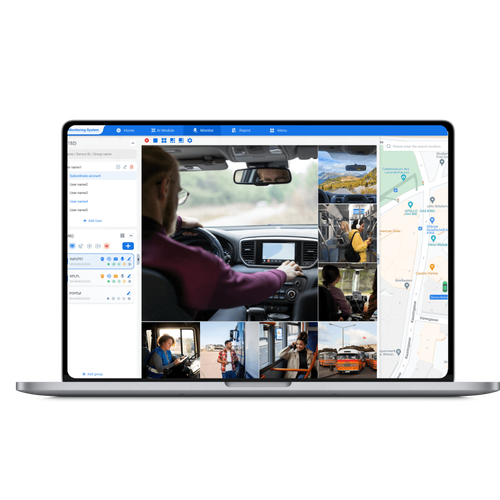
Fixes must be explicit, testable, and minimal in blast radius:- Strong device identity: X.509 certificates or hardware-backed keys for each unit.- Encrypted links: TLS with mutual authentication for telemetry and command channels.- Network micro-segmentation: isolate control plane, telemetry, and maintenance access.- Least-privilege authorization: role-based access tied to short-lived tokens.- Tamper evidence: secure boot and firmware integrity checks.Where orchestration is needed, integrate mature fleet telematics solutions that separate topology configuration from operator privileges. That separation reduces human error and provides audit trails for every critical action.
Operational controls and governance
Technology alone will not suffice. Implement these operational disciplines:- Onboarding workflows with multi-party approvals.- Regular key rotation and revoked-list propagation.- Scheduled penetration tests that include physical-device scenarios.- Clear incident playbooks aligning field crews, control-room staff, and IT.Accountability must be precise. Define who may issue overrides and require multi-person authorization for any command that alters a vehicle’s motion envelope.
Privacy and compliance in plain terms
Treat location and personnel data as sensitive by default. Apply these straightforward rules:- Collect only what operations require.- Store identifiable data encrypted at rest with access logging.- Map data retention to operational needs and legal obligations such as GDPR where relevant.Privacy is a constraint, not a nuisance. Respect it and you reduce insider risk and legal exposure.
Common pitfalls to avoid
Operators repeat the same mistakes:- Trusting a single “secure” vendor without independent verification.- Using broad maintenance accounts rather than ephemeral credentials.- Skipping firmware updates because they “disrupt operations.”Address these with contractual security requirements, automated update windows, and verifiable attestations of security practice.
Evaluating alternatives: pragmatic trade-offs
Choices are rarely binary. Consider three paths:- Build: full control but heavy engineering and lifecycle burden.- Buy a platform: faster deployment, variable transparency.- Hybrid: core controls built in-house, telemetry and analytics outsourced.Each path demands the same controls: identity, segmentation, and auditable access. Pick the path that matches your team’s capacity to maintain rigorous security hygiene.
Implementation checklist
Begin with these concrete steps:- Inventory all devices and software components.- Profile data flows and map privilege boundaries.- Deploy mutual-TLS for control channels within 90 days.- Require multi-factor authentication and short-lived tokens for human access.- Conduct tabletop exercises simulating lost keys or command-channel hijack.
Synthesis and the practical value
When the problem is named and the fixes are simple, resilience follows. Clear identities, strict boundaries, and accountable operations stop most attacks and prevent dangerous mistakes. That combination is the design principle behind trusted deployments and it’s exactly the competence the market expects from established providers; the pragmatic integration of these elements is what defines BSJ in field practice — informed, precise, and aligned with the needs of those who move ore and keep people safe.